
PHP website security, checked and documented
Know where your website stands.
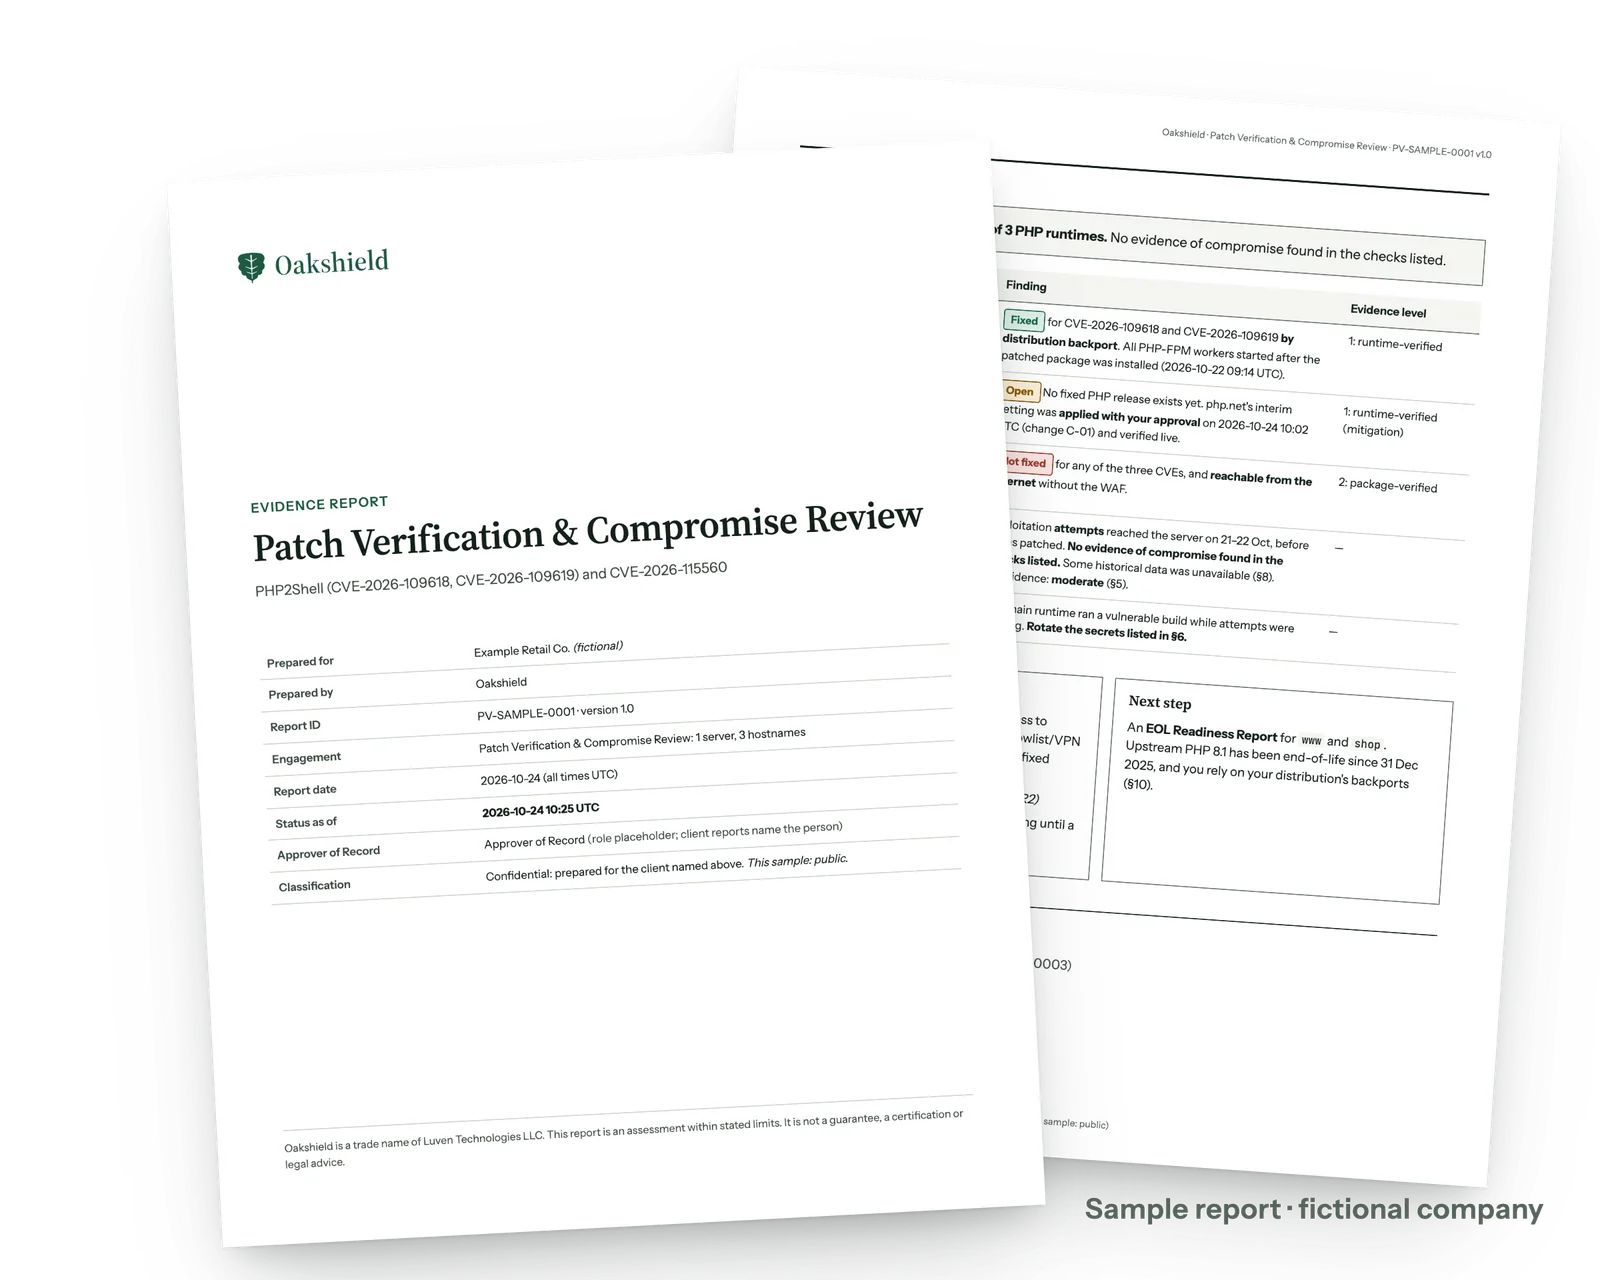
We check that October’s PHP security fixes are installed and running on your server, look for signs of a break-in, and sign a plain-English report.
We reply within 1 business day.
PHP 8.2 stops getting security fixes on (source: php.net supported versions).
CVE-2026-115560 isn’t fixed by October’s PHP releases (source: php.net advisory on CVE-2026-115560, October 23, 2026). PHP recommends one setting until its next release, and says exploitation is unlikely.
What we offer
Fixed scope, published prices, written authorization before any access, and a signed report at the end.
-
Patch Verification & Compromise Review
Am I patched, and are there signs anyone got in? A signed report you can forward: the status of each fix, and a review with every check listed.
$590 per server, includes 1 site
Book a call -
Verification Plan
Show patch status over time, not once: quarterly re-verification, and a re-check after the next critical PHP flaw.
$990 per server per year
Book a call -
Agency Fleet Triage
One clear call per client site, and a one-pager for each client site under your name.
From $99 per site; 10-site pilot $990
Book a call -
EOL Readiness Report
Will your site run on PHP 8.4, and what will the move take?
From $290 per site
Book a call
How it works
-
Agree what we’ll check
Tell us your site. You authorize the scope in writing before we start.
-
Give us read-only access
Your developer or host shares a read-only login through a secure link.
-
Get your report
1 business day after access works: a signed report and next steps.
What you get
One report, written for the people who make the decisions.

A one-page summary in plain English.
A clear status for every issue.
A check for signs of a break-in.
Next steps, and who signed off.
Who it’s for
Online stores
Card payments raise the stakes. Payment-page and skimmer checks are not included.
What you can count on
Nothing happens without your written OK.
-
A named person signs off.
Prices are published, and they don’t change in a crisis.
-
We practise what we recommend.
Check for yourself: Our security practices Where every figure comes from
Questions
My host manages my website. Do I need this?
Maybe not. Many hosting companies reported updating PHP on their managed plans (source above). Ask them to confirm in writing; here’s an email you can send. If you need proof for a customer or insurer, our report can record their confirmation.
Why can’t my developer just check the version number?
Because the number often doesn’t change when the fix is installed, and the fix only takes effect after a restart. Our report checks what’s actually running.
What if the report finds a problem?
It tells you exactly what needs doing, in order. If we find signs that someone got in, we stop, keep the evidence, contact you, and recommend next steps.
What if you can’t tell?
Then the report says so, with the reason and how to find out.
Is this a one-off?
It can be. Or choose the Verification Plan ($990 per server per year): we check again every quarter, and after any new critical PHP alert that affects your server.
Who is Oakshield?
A software-engineering and security firm. Oakshield is a business of Luven Technologies LLC. You can reach us at hello@oakshield.co.
For technical teams: CVE details, how we verify a fix, and evidence levels are in our technical briefing.
Your website, accounted for.
Find out where your website stands.
We reply within 1 business day.
Sources
Every figure and quotation on this page links to its primary source. All of them, with the date we last checked each: full wording and methods.
-
PHP 8.2 end of life S-32
Last checked: October 23, 2026
-
CVE-2026-115560: not fixed by the 21 Oct releases S-02b
php.net advisory on CVE-2026-115560, October 23, 2026 CERT-EU BleepingComputer Cloudflare
Last checked: October 23, 2026